
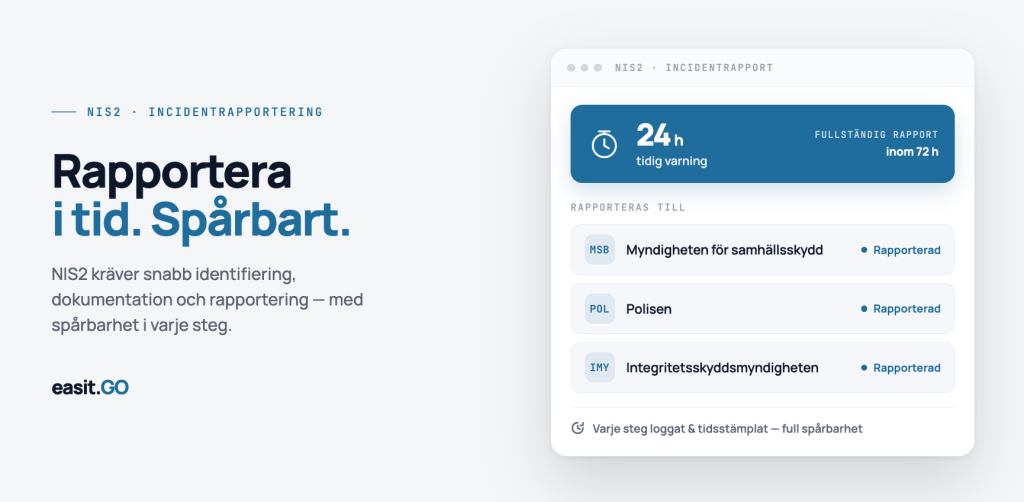
With the NIS2 Directive, Sweden has stricter requirements for how serious and reportable incidents should be handled. Organizations covered by the Directive must be able to report an incident within 24 hours to the Swedish National Security Agency, the Police and the Swedish Data Protection Authority.
To make it easier for our customers, we have developed a ready-made incident process in Easit GO for cybersecurity incidents, structured in clear steps that follow MSB's guidelines and NIS2's reporting requirements.
What is a serious and reportable incident?
Unlike everyday IT incidents, such as login problems or a broken printer, these are incidents that can have a significant impact on the delivery of essential or digital services.
According to MSB, this could include, for example,
- Major outages that affect availability for a longer period of time.
- Cyberattacks that lead to intrusions, data leaks or manipulation of information.
- Incidents that compromise confidentiality or integrity, such as exposure of sensitive personal data.
- Disruption of critical functions where the business can no longer deliver its services.
The reporting obligation includes both an initial report within 6 hours and a follow-up report with more detailed analysis when more facts are available.
New incident process in GO (Cybersecurity Incident)
To meet these requirements, we have built a process into GO that is divided into six steps:
- Initial assessment – quickly assess the scope of the incident and determine if it is reportable.
- Initial actions & management – take the first steps to limit damage and restore operations.
- Reporting – use ready-made templates to create reports to MSB, the Police and IMY.
- Risk and safety analysis – analyze causes, consequences and lessons learned.
- Follow-up and improvement measures – document how the incident was handled and how future risks can be reduced.
- Files & history – collect reports, attachments and documentation in one place for full traceability.
Why is this important?
Having a structured process for serious and reportable incidents is crucial to meeting NIS2 requirements. But it is also a matter of business resilience.
- Faster recovery reduces the risk of long-term operational disruptions.
- Traceability and transparency create security when interacting with authorities.
- Systematic learning strengthens the organization's ability to deal with future incidents.
With GO's incident process, organizations receive practical support that combines operational management, reporting obligations and improvement work - in one solution.
Want to see how the process works in practice? Contact us for a demo.
Henrik Traveler
Commercial Product Manager
henrik.resare@easit.com
+46 70 249 36 06